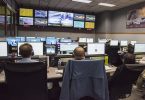
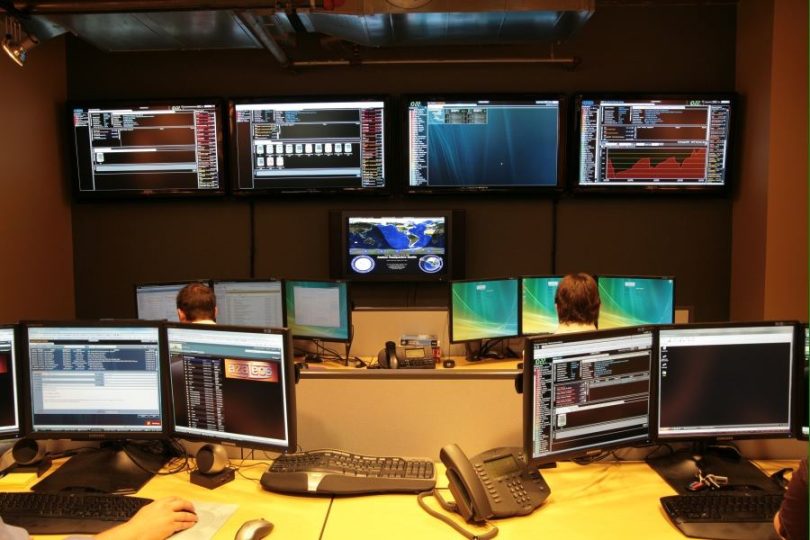

A security operations centre rarely sleeps, even when the offices around it are dark and quiet. Through the night, analysts watch dashboards that gather login attempts, network traffic and software alerts from hundreds of systems at once. Most signals turn out to be harmless, such as a forgotten password or an automatic update arriving at an unusual hour. The real skill lies in spotting the few patterns that do not fit, and then checking them calmly before they grow into something larger. Teams work in rotating shifts, hand over detailed notes, and keep a shared record so that nothing important is lost between one group and the next. It is patient, methodical work rather than drama. Shift handovers are treated as seriously as any alert, with outgoing analysts walking their replacements through open cases, odd patterns and systems already checked.
What the Evidence Shows
Modern centres rely on automation to sort the routine from the risky, flagging unusual behaviour for a human to review first. Analysts then trace where a suspicious file came from, which accounts it touched, and whether any data actually left the network. Clear playbooks help the team act quickly without guessing, isolating an affected laptop while keeping the rest of the business running. Regular reviews after quiet nights matter too, because they reveal weak passwords, outdated software and settings that drift over time. For smaller organisations that cannot staff a centre alone, shared services now offer the same watchful eye around the clock. After an incident closes, the team holds a short review to ask what worked, what slowed them down and what should change in the playbook. Those lessons are written down while memories are fresh, then tested in later training exercises. Over months, that steady habit of reviewing and refining is what turns a room full of screens into a genuinely dependable line of defence. Reporting and analysis from sources such as IEEE Spectrum track the same developments, and specialists following security operations centre say the direction is now consistent across independent lines of evidence.
The Wider Context
Adoption of security operations centre follows a familiar pattern with an unfamiliar speed. Early users tolerate rough edges in exchange for advantage, mainstream users arrive when the tool disappears into existing workflows, and the market consolidates around whoever made that transition feel effortless. Vendors are racing less on raw performance now than on integration, support and trust.
What Happens Next
The realistic forecast for security operations centre is steady integration rather than sudden replacement: embedded in products people already use, improving in increments, and regulated in proportion to its reach. The companies and institutions that plan on that basis, training staff and redesigning processes instead of chasing launches, are the ones the adoption data tends to vindicate. You can follow related developments in our coverage of technology.
It is also worth remembering how quickly the picture in this area has changed before. Positions that looked settled a few years ago have been revised as new data arrived, and the same humility is appropriate now. The strongest coverage of this subject, and the most useful advice, tends to come from sources that update their views openly when the facts move, rather than defending an earlier position long after it has stopped fitting the evidence available.